
We help organisations test their cyber resilience
CREDS is a Dutch offensive security company, based in Utrecht since 2019. We show organisations what would actually happen if they were attacked, by attacking them ourselves, safely and under control. We prove which weaknesses can really be exploited to reach your crown jewels and how to fix them.
For organisations that know security goes beyond a firewall
CREDS is there for every organisation that wants to be sure their digital security works well. For IT managers, security specialists and compliance employees who don't want to waste time on superficial security scans. Traditional penetration tests are often expensive, take a lot of time and leave important risks. Meanwhile, hackers keep thinking of smarter ways to penetrate your systems.
What you can expect from our smart security solutions



Advanced attacks, no simulations
Test your security with the scenarios real attackers use, including ransomware and phishing.

Direct insight into vulnerabilities
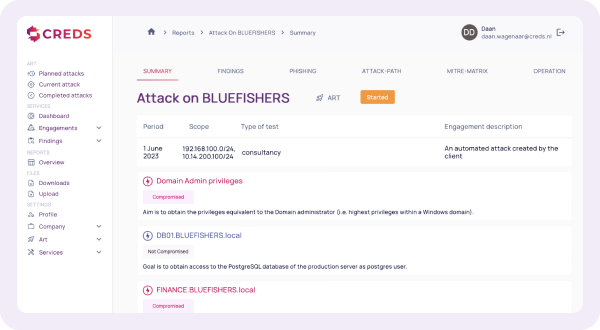
Real-time reports show where you are at risk, with concrete improvement suggestions.

Always available without installation
Plug & play platform without software agents or IT resources. Start when you want.

Complies with laws and regulations
Supports DORA, NIS2 and ISO27001 compliance — with demonstrable validation.

Training for your SOC team
Custom purple teaming: your detection and response become structurally better.

Savings on time and costs
No manual penetration tests, expensive consultancy or waiting times — but fast results and clear ROI.
What happens if you do nothing?
If you only see the obvious attacks, you stay blind to the real ones. Scanners and one-off tests surface the obvious, while the paths a real attacker takes stay hidden. The current threat landscape, the pace of AI development and tightening compliance requirements all call for a more thorough approach, one that runs every phase of an attack.
Why should you take action now?
- Know which weaknesses are actually exploitable, not just theoretical
- Test continuously instead of once a year
- Validate that your detection and response actually work
- Prove your resilience to clients, insurers and auditors
- Reduce the cost and lead time of security testing
- Meet DORA, NIS2 and ISO 27001 evidence requirements
Our IoT and SCADA environment can't simply be switched off for security work, so we needed a risk appetite that fits how we actually operate. They defined it with us and then raised our maturity step by step, from level one to level four, without disrupting production. Their monthly attacks show us exactly where to improve next. They also checked our passwords against known data leaks and audited them across our network, which sharply reduced the number of easy-to-guess passwords. Steady, practical progress we can measure.
With a large infrastructure and a lot of IoT, we needed security that grows with us. They have helped us raise our maturity level by level. We run our own phishing platform, but we also use theirs because it achieves a higher hit rate, which has really strengthened user awareness. Every month their attacks test our environment, and after each run their red team delivers a roadmap to make us more resilient against malware. They also perform ransomware attacks seen in the food industry, so we prepare for real threats.
Every quarter they assess our cloud environments and Microsoft 365, benchmark them against industry standards and actively attack them to uncover realistic attack paths. Last year, two of their four attacks reached our crown jewels. That was exactly the honest test of our security measures, on-premise and in the cloud, that we needed. What I value most is the follow-up: they join the report discussions together with our IT partners, so findings turn into concrete actions and continuous improvement actually gets started.
For us, compliance and stakeholder confidence are essential. Their platform runs frequent tests and delivers detailed technical reports for our IT teams, plus tailored reports for our stakeholders and regulators. Internally, that gives us a clear improvement roadmap; externally, it provides the assurance our stakeholders and supervisors expect. We were genuinely impressed by how advanced the attacks were and how often they reached our crown jewels. It is a real red team experience, delivered continuously through their platform, and it keeps us sharp.
CFO, healthcare manufacturing company
IT Partner, food industry supply chain partner
CISO, pension fund
CISO, financial institution
Client names are withheld for confidentiality reasons.
Don't just take our word for it
That's what our clients say and we're proud of it.
Passion for security
- Multidisciplinary team: Reverse engineers, ethical hackers, IT auditors and developers.
- Minimum 10 years experience per team lead.
- Fully established in the Netherlands, infrastructure in Europe and ISO 27001-compliant.
- Only focused on offensive security.
- Strong focus on automation and unique solutions.

See how our platform works and makes your organisation more secure.
Steven Visscher | Channel Partner Manager
Fill out the form and we will contact you soon for an introduction.