
Advanced cyber attacks, on demand and tailored to your organisation
Our team of ethical hackers has channelled its expertise into ART: a platform that attacks organisations in the same way as real criminals do, right down to the crown jewels. Not a scanner, but real attacks.
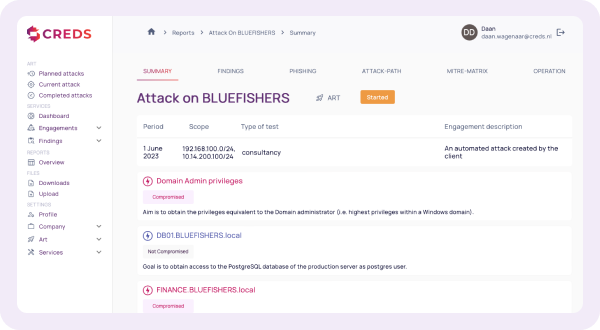
Key features of the CREDS platform
- Advanced cyber attacks with minimal risk
- Identify attack paths to your crown jewels
- Cover all attack phases and perspectives
- Start directly without installation
- Real-time insights and (compliance) reporting
- Purple teaming and SOC training
- Continuous availability and repeatability
Attack approaches within CREDS ART


External attack
CREDS attacks your public IT infrastructure and cloud environment to expose vulnerabilities and identify attack paths.
Phishing campaigns
Advanced phishing emails are sent to test employee awareness and gain access to valuable systems, enriched with OSINT data.
Internal attack
CREDS attacks as if a malicious employee or infected user has internal access, including privilege escalation and protocol manipulation.
Malware escalation
New malware techniques are applied every month to test the resilience of endpoints, cloud and network, without damage but with realistic impact.
Cloud assessment
CREDS attacks your cloud tenants the way an intruder would: Azure, Microsoft 365, Entra ID, AWS, GCP and StackIT, including the connections to your on-premises estate.
Kubernetes escalation
CREDS starts from a single compromised pod and works outward: workload isolation, RBAC, the registry and supply chain, and escape paths to the host or control plane.
From attack path to fix, in one portal
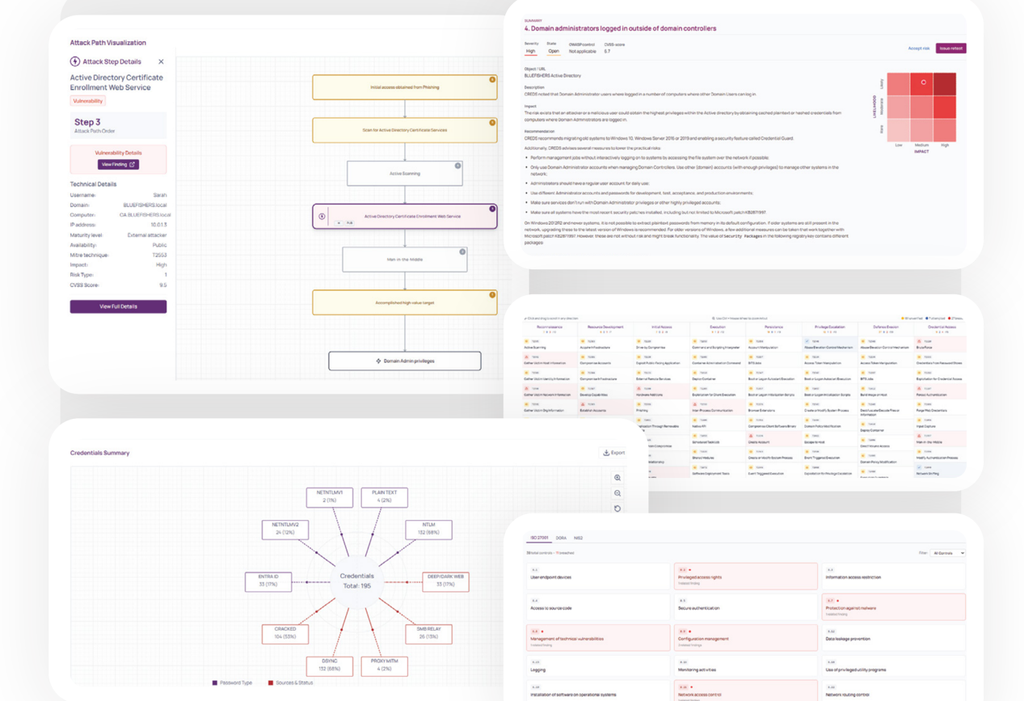
Every attack CREDS runs lands in the portal while it is still running, with the context your team needs to act on it.
- Real-time insight into attack paths, MITRE ATT&CK mapping, leaked credentials, findings, clean up lists and requested approvals.
- Every finding can be examined and mitigated directly, following our recommendations. You can also accept a risk or, where possible, have the effectiveness of a fix reassessed.
- Push findings straight to your ticket system (Jira, ServiceNow, YouTrack and others) or to your SIEM and SOC tooling.
Every attack results in three reports
Each report is written for a different audience, so the same attack serves your engineers, your management and your auditors.
- Detailed report: all findings with the technical detail needed to mitigate them.
- Client abstract: a management summary without detailed advice, covering only the highlights, so it can be shared with internal and external stakeholders.
- Compliance report: written from a compliance perspective, against the control frameworks your organisation uses.
Our IoT and SCADA environment can't simply be switched off for security work, so we needed a risk appetite that fits how we actually operate. They defined it with us and then raised our maturity step by step, from level one to level four, without disrupting production. Their monthly attacks show us exactly where to improve next. They also checked our passwords against known data leaks and audited them across our network, which sharply reduced the number of easy-to-guess passwords. Steady, practical progress we can measure.
With a large infrastructure and a lot of IoT, we needed security that grows with us. They have helped us raise our maturity level by level. We run our own phishing platform, but we also use theirs because it achieves a higher hit rate, which has really strengthened user awareness. Every month their attacks test our environment, and after each run their red team delivers a roadmap to make us more resilient against malware. They also perform ransomware attacks seen in the food industry, so we prepare for real threats.
Every quarter they assess our cloud environments and Microsoft 365, benchmark them against industry standards and actively attack them to uncover realistic attack paths. Last year, two of their four attacks reached our crown jewels. That was exactly the honest test of our security measures, on-premise and in the cloud, that we needed. What I value most is the follow-up: they join the report discussions together with our IT partners, so findings turn into concrete actions and continuous improvement actually gets started.
For us, compliance and stakeholder confidence are essential. Their platform runs frequent tests and delivers detailed technical reports for our IT teams, plus tailored reports for our stakeholders and regulators. Internally, that gives us a clear improvement roadmap; externally, it provides the assurance our stakeholders and supervisors expect. We were genuinely impressed by how advanced the attacks were and how often they reached our crown jewels. It is a real red team experience, delivered continuously through their platform, and it keeps us sharp.
CFO, healthcare manufacturing company
IT Partner, food industry supply chain partner
CISO, pension fund
CISO, financial institution
Client names are withheld for confidentiality reasons.
Don't just take our word for it
That's what our clients say and we're proud of it.
What makes CREDS ART better



See how our platform works and makes your organisation more secure.
Steven Visscher | Channel Partner Manager
Fill out the form and we will contact you soon for an introduction.
Questions & answers
CREDS offers automated, continuous security testing instead of one-time manual penetration tests. Our technology carries out real attacks 24/7 without installation, while traditional penetration tests often take months and only provide a snapshot.
Yes, within the limits you set. You define the scope and a risk appetite per asset, and a panic button stops any attack immediately. ART shows every active friendly virus and gives you a clean-up list if changes were needed. Our friendly viruses are built in-house to strict coding guidelines, our architecture follows a safe to fail principle, and we never attack without signed authorisation.
You decide what is tested, how far an attack may go and when it runs. Scope and risk appetite are set per asset before anything starts. Every active attack is visible in the portal, together with a clean-up list of any changes made. The panic button stops all activity immediately if required.
CREDS provides a small computer, an Intel NUC, which you place on your internal network for the duration of the engagement. Placing that device is the only thing required: no software is installed on your systems and no agents are rolled out. The computer is temporary and is returned once the engagement ends.
CREDS ART performs a wide range of real cyber attacks, including ransomware, phishing, SQL injection, cross-site scripting (XSS), and advanced persistent threats (APT). Our platform uses current attack techniques that hackers actually use.
Real-time insight in the CREDS ART portal while the attack is still running, plus three reports. The detailed report lists all findings with the technical detail needed to mitigate them. The client abstract is a management summary of the highlights, written to be shared with internal and external stakeholders. The compliance report covers the same attack against the control frameworks your organisation uses.
Yes. Once you have fixed a finding you can re-run the attack to confirm the path is closed. Retests are included and you can run them at any time, as often as you need. Not all findings can be retested, only findings that do not rely on a specific attack path can be retested.
CREDS ART identifies security risks, reports them and turns them into concrete action points, with results you can map directly to DORA, NIS2 and ISO 27001 requirements. This lets you show that you test and manage risk structurally. CREDS ART supports your compliance, it does not certify it.
All data from your attacks is hosted in the EU. CREDS itself is ISO 27001 certified. Our trust center lists the certifications we hold, and the underlying control framework is available on request. All data of the attack is removed within two weeks after the report is issued. The report itself is preserved, on request the report can also be removed.
No. CREDS ART handles continuous, repeatable testing at scale, so your baseline stays current between engagements. For unique systems, complex applications or scenario-based red teaming, our specialists add manual testing. Our red teaming and web application testing pages cover that work.
A vulnerability scanner reports possible weaknesses. CREDS ART actually exploits them and chains them into attack paths, so you see what an attacker can really reach. Breach and attack simulation (BAS) tools only imitate attacker behaviour, while CREDS ART carries out real attacks.
No, CREDS is suitable for organisations of any size. Our platform scales with your infrastructure and needs. Whether you're an SME or a large enterprise, CREDS offers appropriate security testing for your situation.
You can start with CREDS within a few days. Our plug & play platform requires no software installation or complex configuration. After a short onboarding and scope determination, you can immediately start testing.
CREDS offers purple teaming with different maturity levels where your SOC team learns from realistic attack scenarios. By performing real attacks, your team structurally improves their detection and response capabilities, making them better prepared for actual threats.